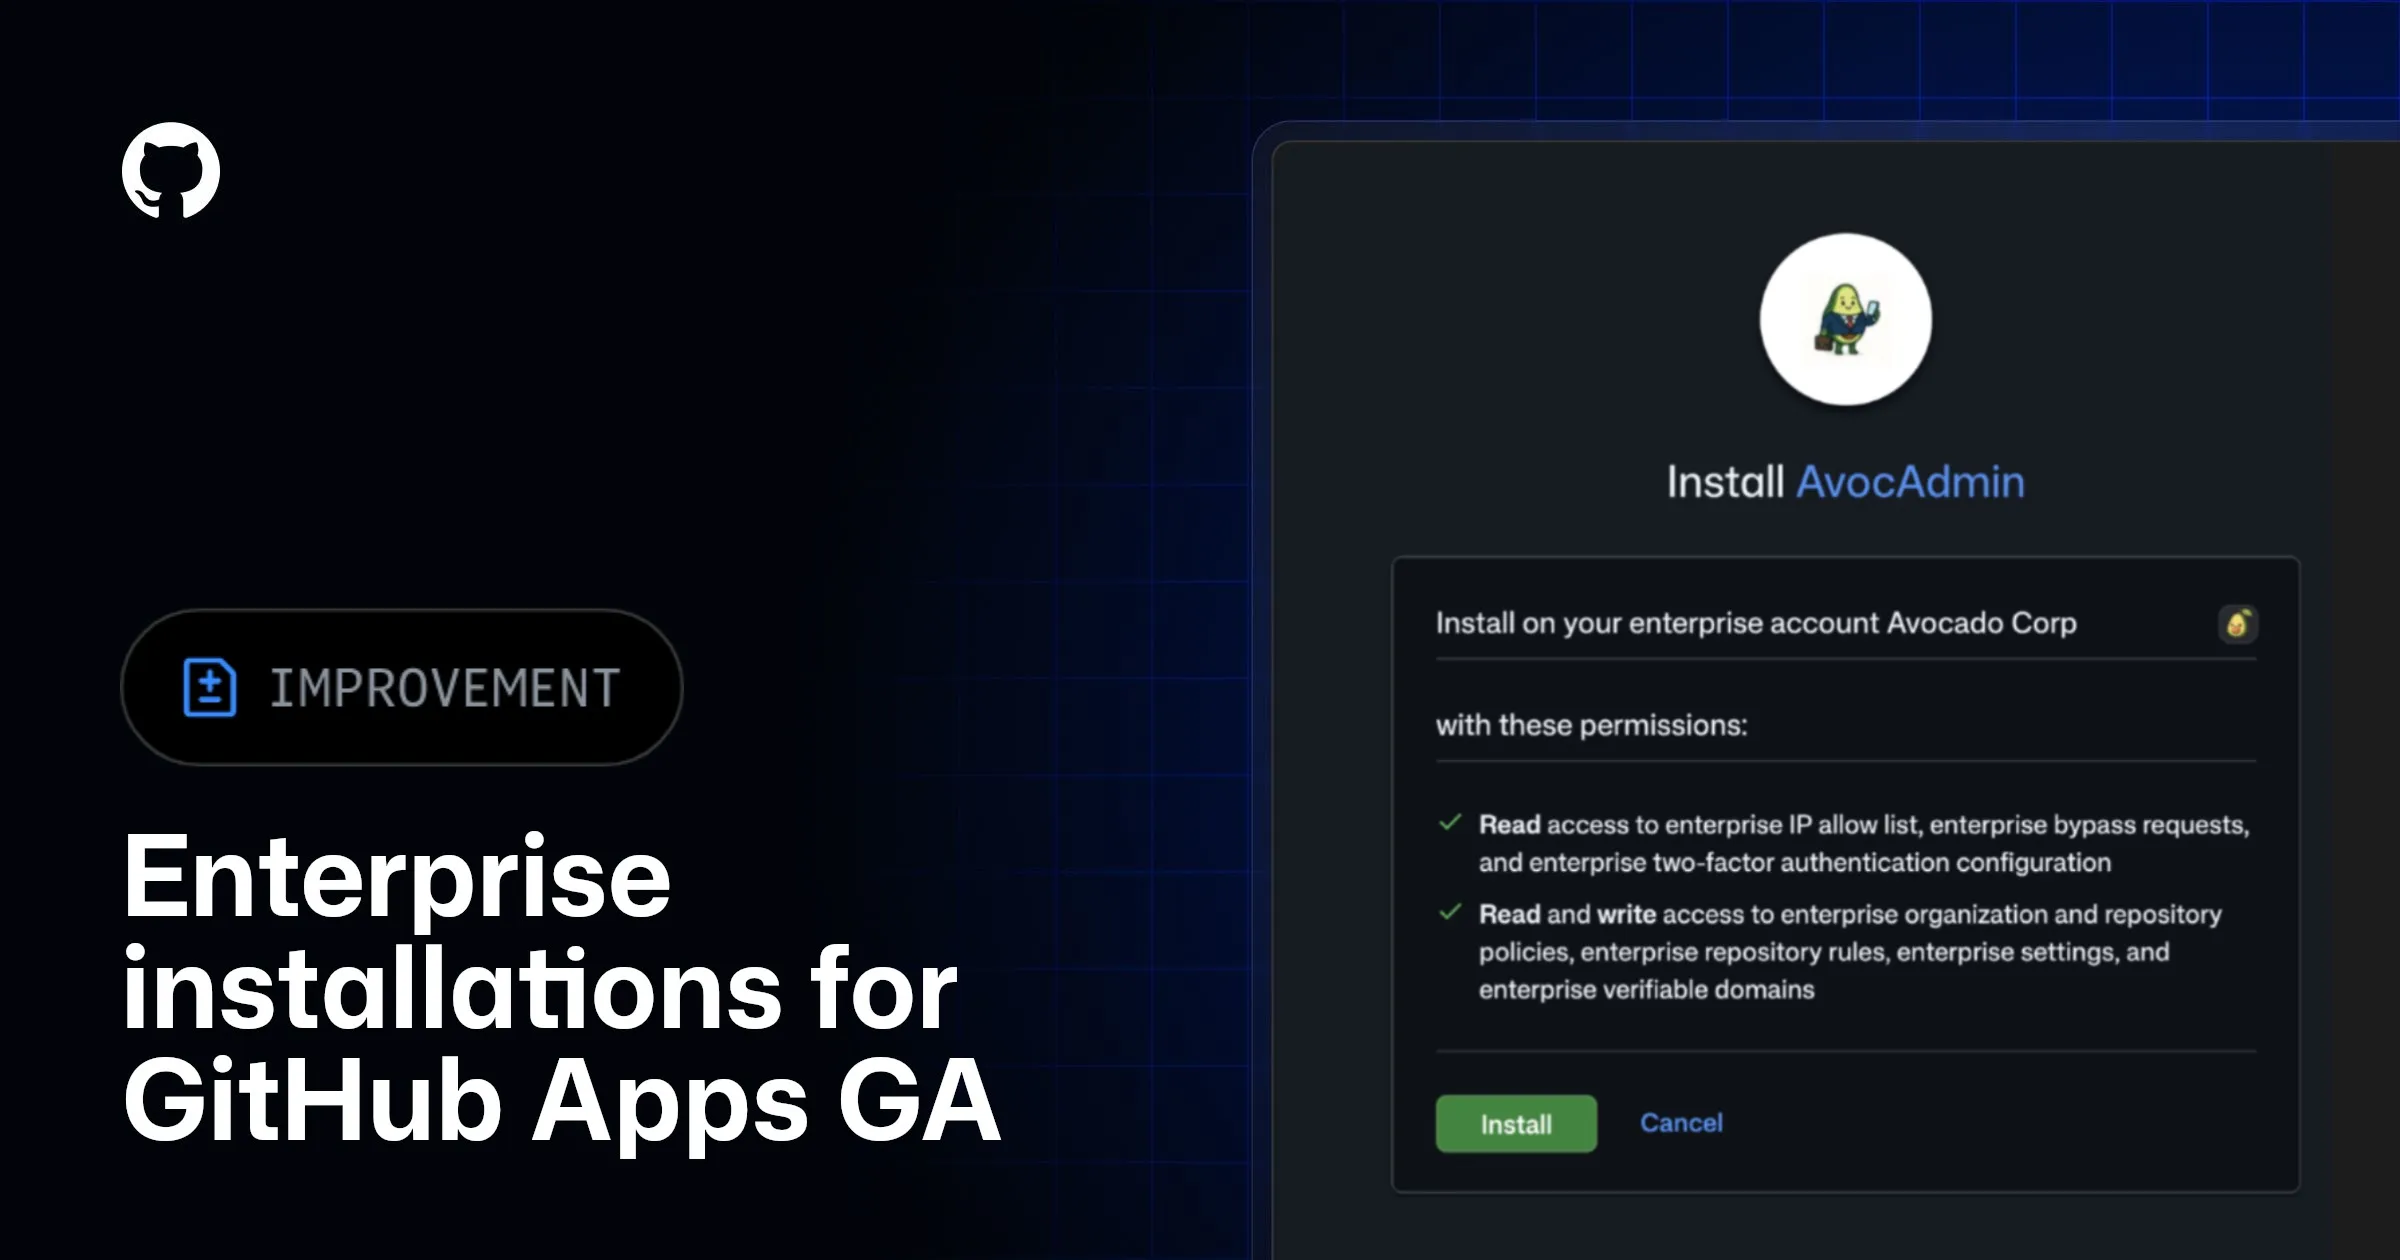
GitHub's second notable October 23 release expands GitHub App installations at the enterprise level from preview to general availability. The newly supported permissions include repository policies, enterprise rulesets, two-factor authentication requirements, verified domains and IP allowlists. The appeal is permissioned automation that does not depend on a long-lived personal access token belonging to an employee.
The release is enterprise-focused; it does not magically add those administrative controls to a personal or small-team plan. But the underlying design pattern matters for any consulting or SaaS integration: use narrowly scoped app identities, not a developer's personal credential, whenever automation will run unattended. That reduces the damage from leaked keys and makes ownership easier to transfer.
If an enterprise client is still using classic personal access tokens for repository governance, the new permissions may justify a migration plan. Map each existing token to the API calls it makes, check which GitHub App permission covers them, and migrate a single low-risk automation first. The payoff is a cleaner access model and fewer secrets tied to individual people.