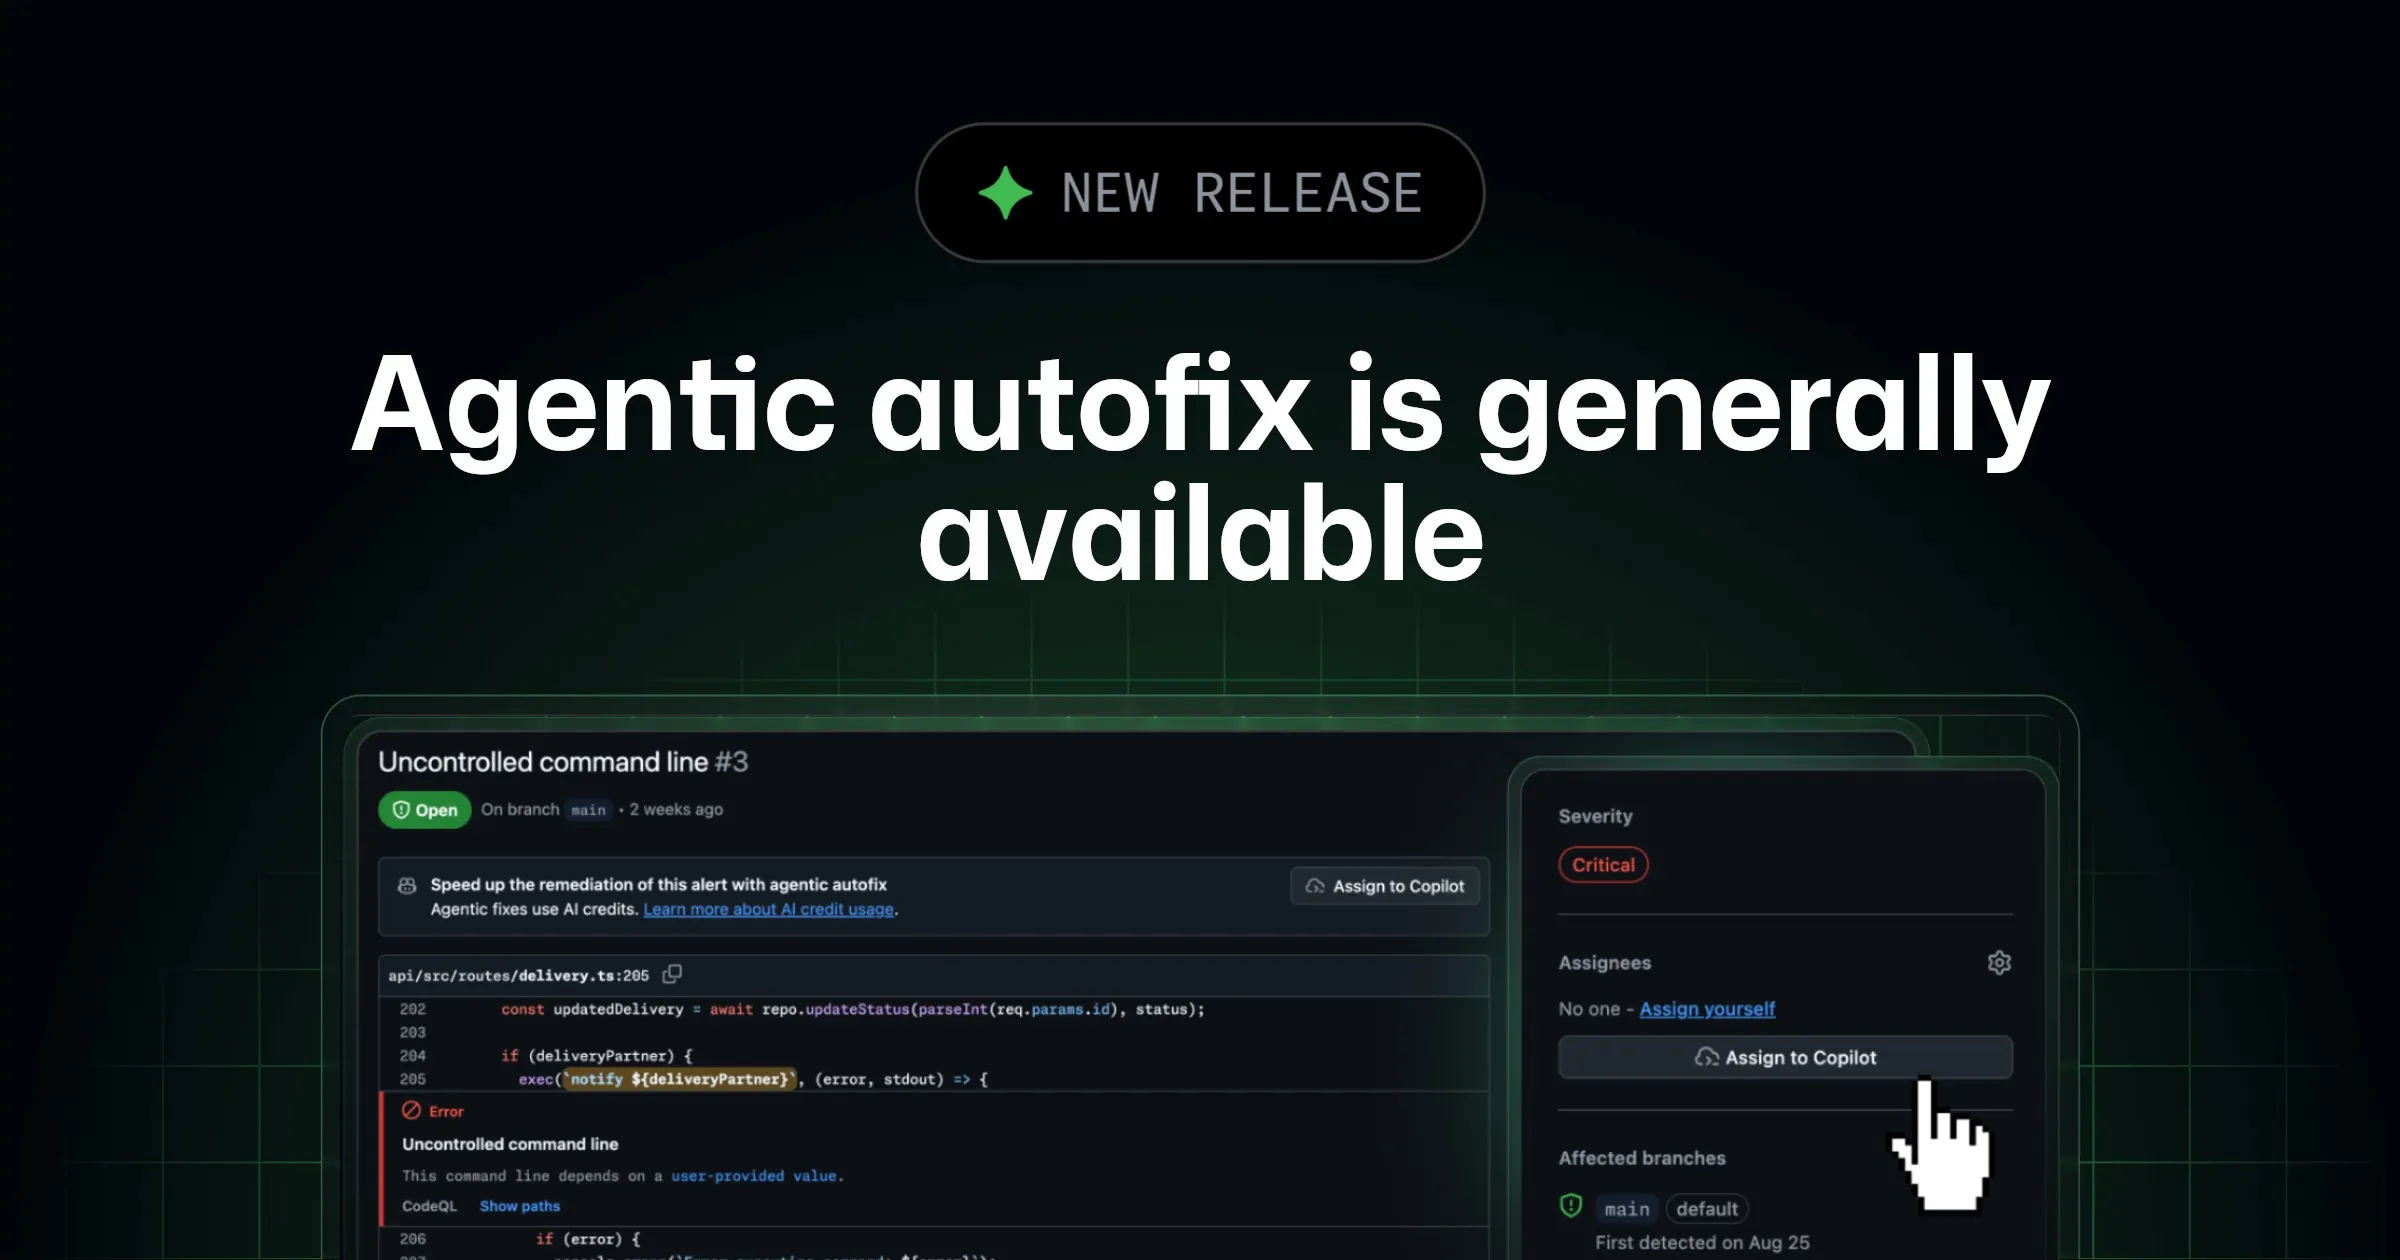
GitHub separately made agentic autofix for code-scanning alerts generally available on October 15. A developer can assign a supported default-branch alert to Copilot, which explores relevant code, proposes a fix and validates it by rerunning CodeQL.
The output is a draft pull request, not an automatic production change. Teams can select up to 25 alerts for one remediation job, then inspect the proposed code and validation summary.
This capability is gated: it requires Code Security or Advanced Security on Enterprise Cloud, an enterprise policy enablement and a defined Copilot billing method. AI Credits and Actions minutes are consumed.
The best small-team use case is clearing an existing backlog with a human review gate. It is not something to enable blindly on all projects; check eligibility and compare agent output with a manual fix for one low-risk alert.
What to do: If an eligible GitHub organization has a code-scanning backlog, assign one low-risk alert to Copilot and review the draft PR and credit usage.