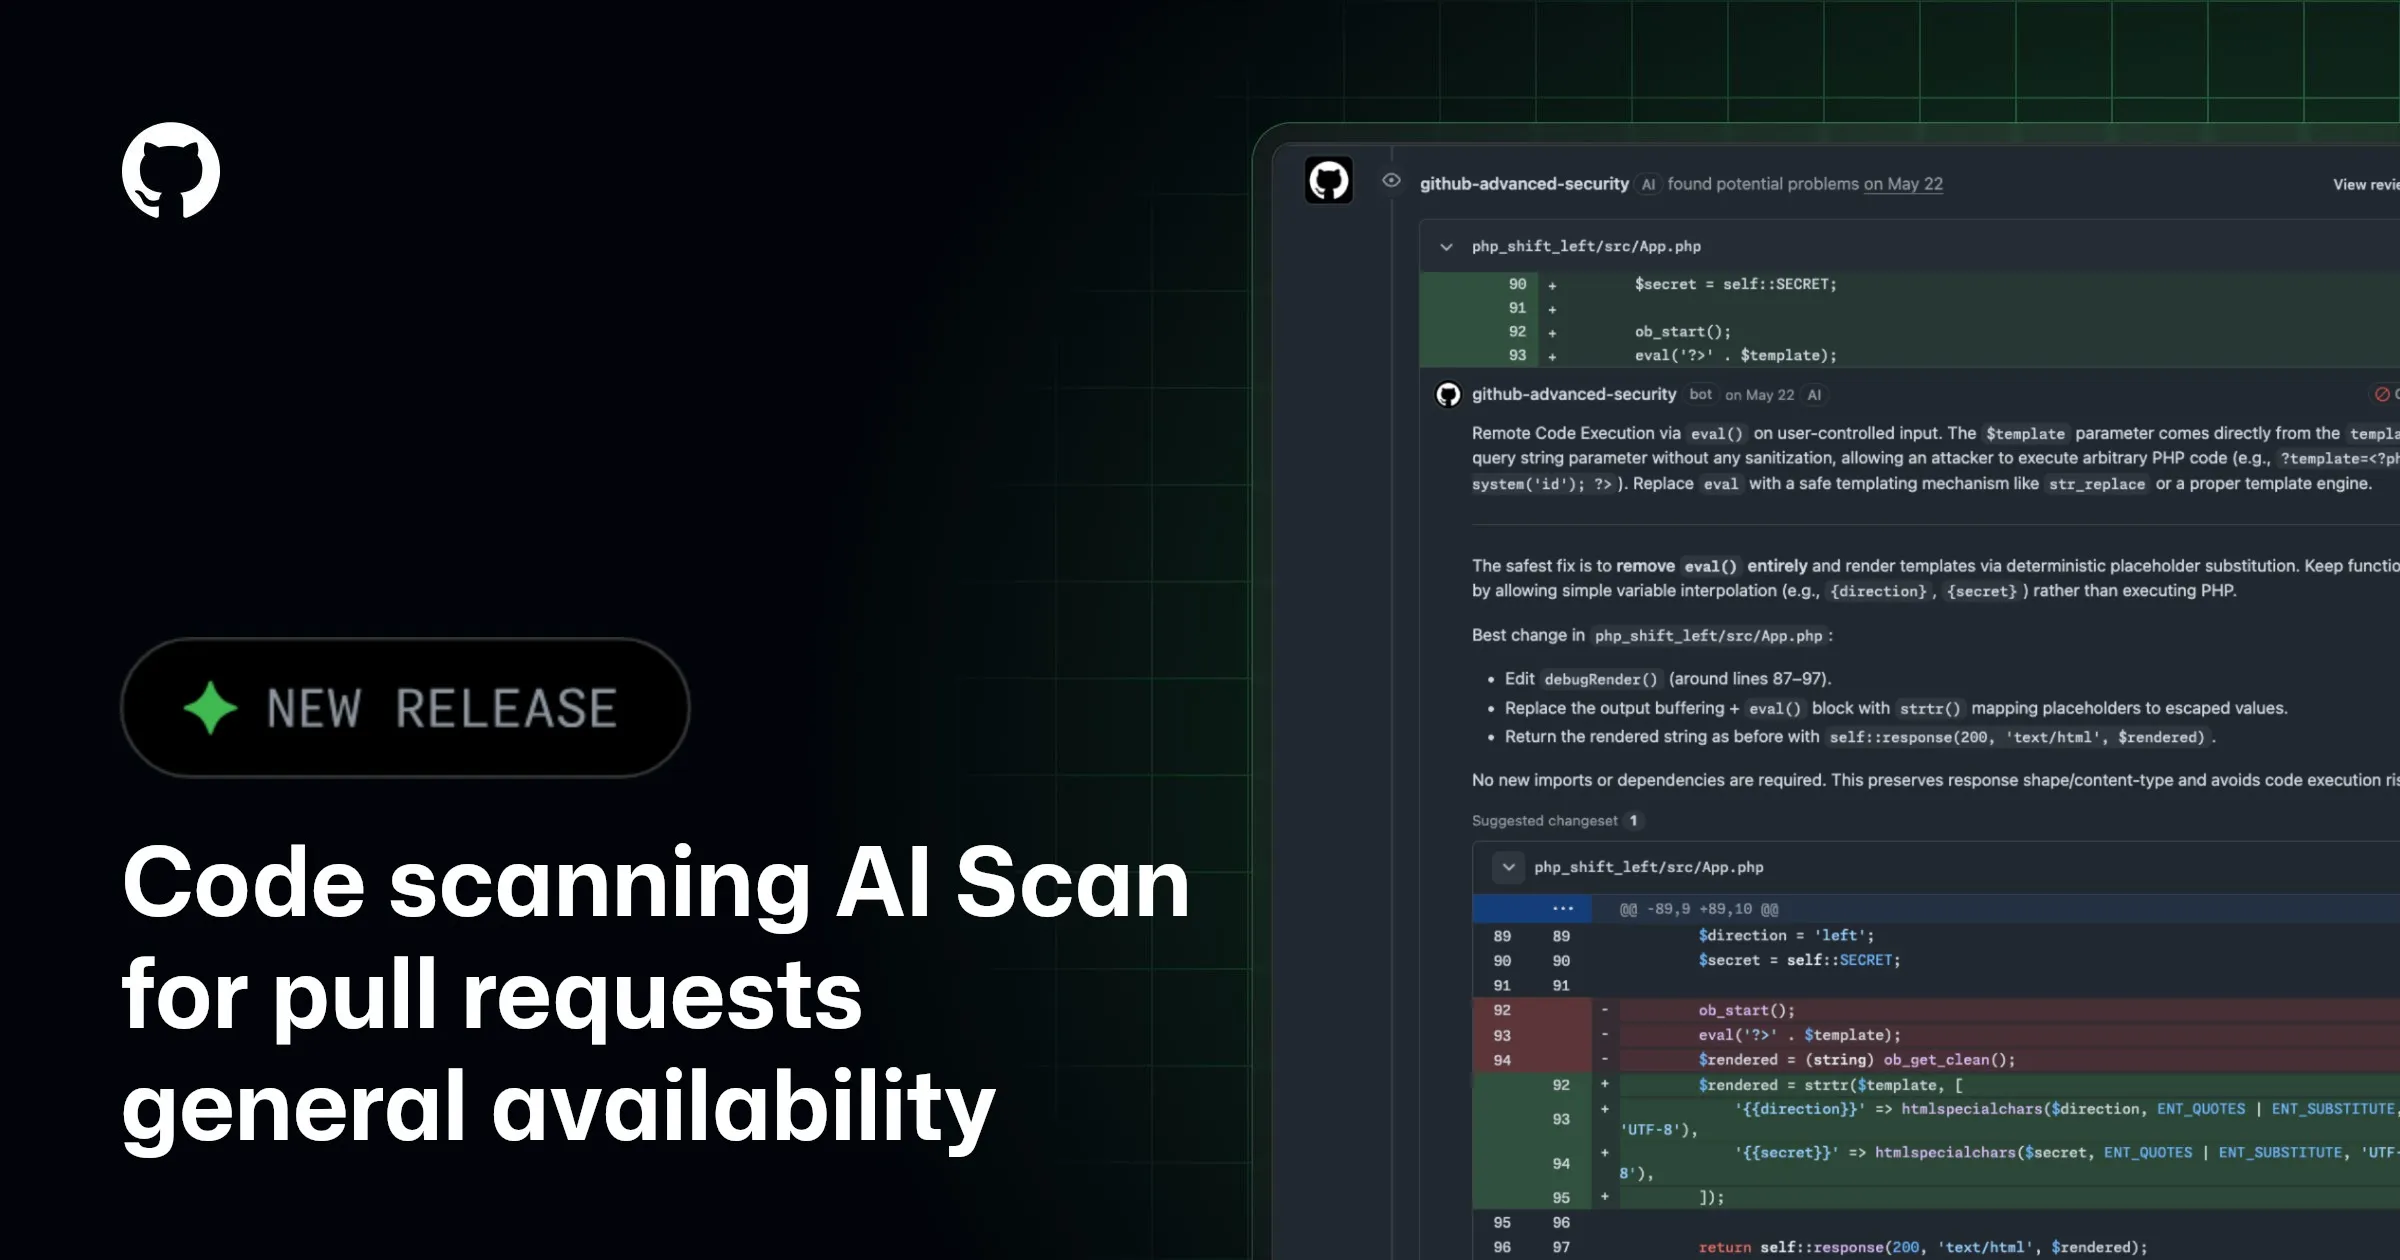
GitHub made AI Scan for pull requests generally available October 15. It complements, rather than replaces, CodeQL. That is especially relevant for small teams whose application code is only part of their attack surface: deployment scripts, container definitions and infrastructure files can introduce problems too.
With code scanning and the effective AI Scan setting enabled, findings appear directly on pull requests, in Conversation and Files changed. GitHub labels AI-generated findings and can offer explanations and suggested fixes. It specifically names PHP, Shell/Bash, Terraform HCL, Dockerfiles, JSP and Blazor among the added coverage.
There are important limits. AI Scan findings are advisory; they do not fail the code-scanning check or block a merge through branch rules. GitHub also says it does not run on pull requests from forks or Dependabot. A clean AI Scan result is not a guarantee that a repository is secure.
Availability differs by repository type. Public repositories under personal or organization accounts are eligible. Private and internal organization-owned repositories require GitHub Code Security or Advanced Security. A Copilot license is not required, but Code Security AI Credits are consumed; the AI-usage billing view and budgets are worth checking.
The sensible first experiment is not a sweeping security program. Pick a low-risk public repository, enable code scanning and AI Scan where the settings allow, then create a small pull request that touches a shell script or Dockerfile. Confirm whether findings arrive in the review flow and whether the explanations are actionable.
For Wake Up, HomeControl and other small projects, this is potentially useful as an additional review layer. Keep existing tests, dependency checks and human review intact; treat the AI signal as a second set of eyes, not as a replacement for engineering judgment.
A meaningful outcome would be a documented security-review workflow that takes minutes rather than a new dashboard that never gets checked. The value is in making the feedback visible at the moment code is about to merge.
What to do: Inspect the GitHub AI Scan eligibility and billing page; test it on one eligible, low-risk repository pull request before considering private-project rollout.